
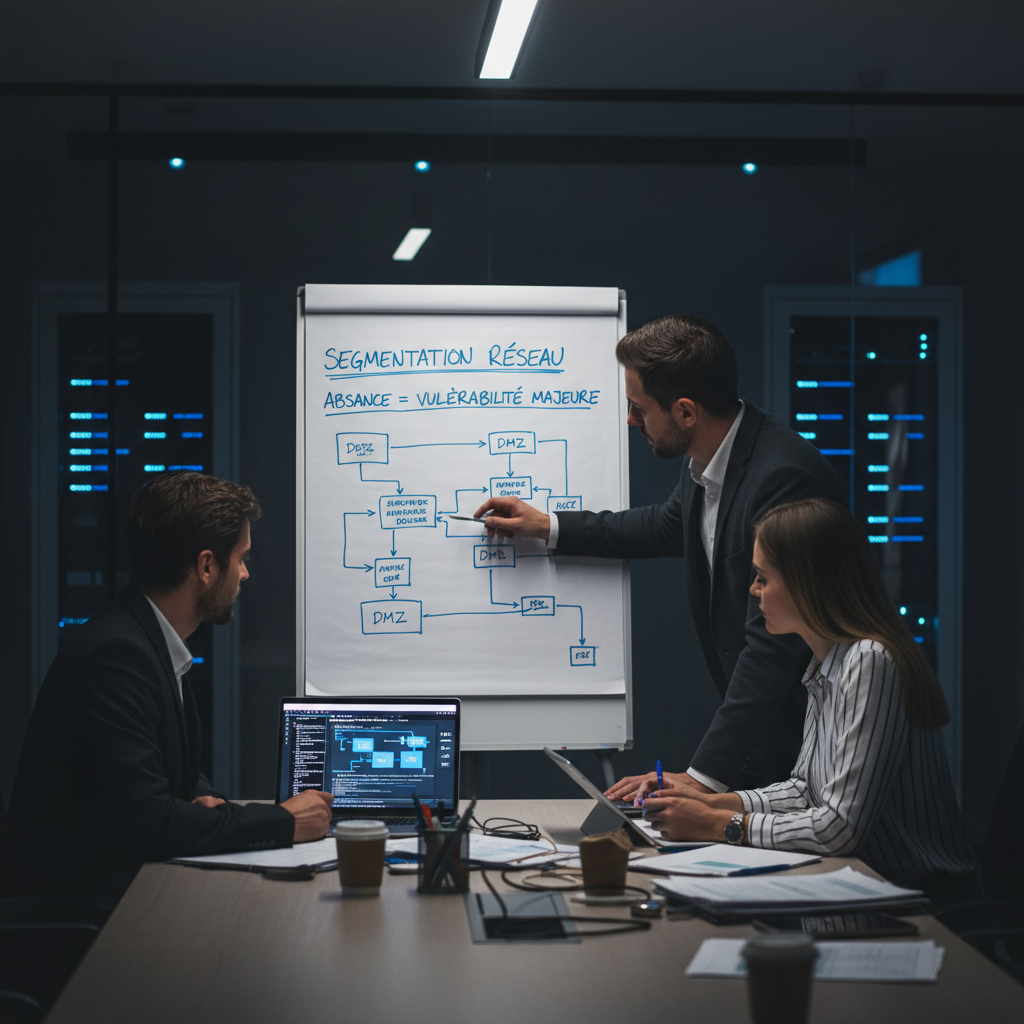
Understanding Network Segmentation and Its Stakes
What is Network Segmentation?
Network segmentation involves dividing a computer network into smaller, isolated subnets. Each segment acts as a distinct security zone, limiting the scope of a potential breach. The goal is to control traffic between these segments, thereby preventing unauthorized access to sensitive data.
Without segmentation, a successful attack on a single point can quickly compromise the entire system. Attackers can move laterally with disconcerting ease, access critical data, deploy ransomware, or exfiltrate confidential information. This issue is particularly concerning for VPS owners who host critical business applications.
The Risks of an Unsegmented Infrastructure
The absence of segmentation creates an extensive and difficult-to-defend attack surface. A well-thought-out segmentation strategy enhances security by isolating critical systems, limiting threat propagation, facilitating regulatory compliance, and optimizing network performance.
🛡️ Strengthen Your Defenses
Discover how tailored network segmentation can drastically reduce your exposure to cyberattacks.
Security AuditThe Pillars of an Effective Segmentation Strategy
Micro-segmentation: A Granular Approach
Micro-segmentation goes beyond traditional segmentation by isolating individual workloads or applications. It creates very fine-grained security policies, tailored to the specific needs of each element, offering maximum protection against lateral movement.
This approach effectively secures a VPS by creating isolation zones for each hosted service or application. Connections between these zones are strictly controlled according to predefined rules.
Segmentation Technologies and Tools
Various technologies enable segmentation implementation, including next-generation firewalls (NGFWs), virtual local area networks (VLANs), access control lists (ACLs), and software-defined security solutions (SDP). The choice depends on the infrastructure's complexity and security requirements.
For virtualized environments like VPS, software solutions offer particularly suitable flexibility, allowing for dynamic and scalable configuration of security policies.
🔍 Identify Vulnerabilities
Our experts conduct in-depth analyses to uncover your infrastructure's vulnerabilities.
Penetration TestingImplementing and Maintaining Your Network Segmentation
Implementing effective network segmentation follows several key steps to ensure optimal protection of your infrastructure.
| Step | Action |
| Analysis and Mapping | Understand the network architecture, identify critical flows, and define security zones |
| Policy Definition | Establish clear rules based on the principle of least privilege for inter-segment traffic |
| Deployment and Configuration | Implement chosen technologies (firewalls, VLANs, SDP) to enforce policies |
| Testing and Validation | Verify the effectiveness of implemented rules and their impact on performance |
| Continuous Monitoring | Analyze traffic and logs to detect anomalies and adjust policies |
| Maintenance and Adaptation | Adapt segmentation to infrastructure evolutions and new threats |
💡 Personalized Advice
Benefit from tailored support to optimize the protection of your information systems.
Request a QuoteConclusion
The absence of network segmentation is a major security flaw that exposes organizations to considerable risks. This vulnerability is particularly critical for VPS owners who must protect their applications and data. By adopting a strategic approach and implementing the right technologies, it is possible to build robust defenses, limit threat propagation, and effectively protect your digital assets. Segmentation is not an option, but a necessity for resilient cybersecurity.
Security Audit
Read more